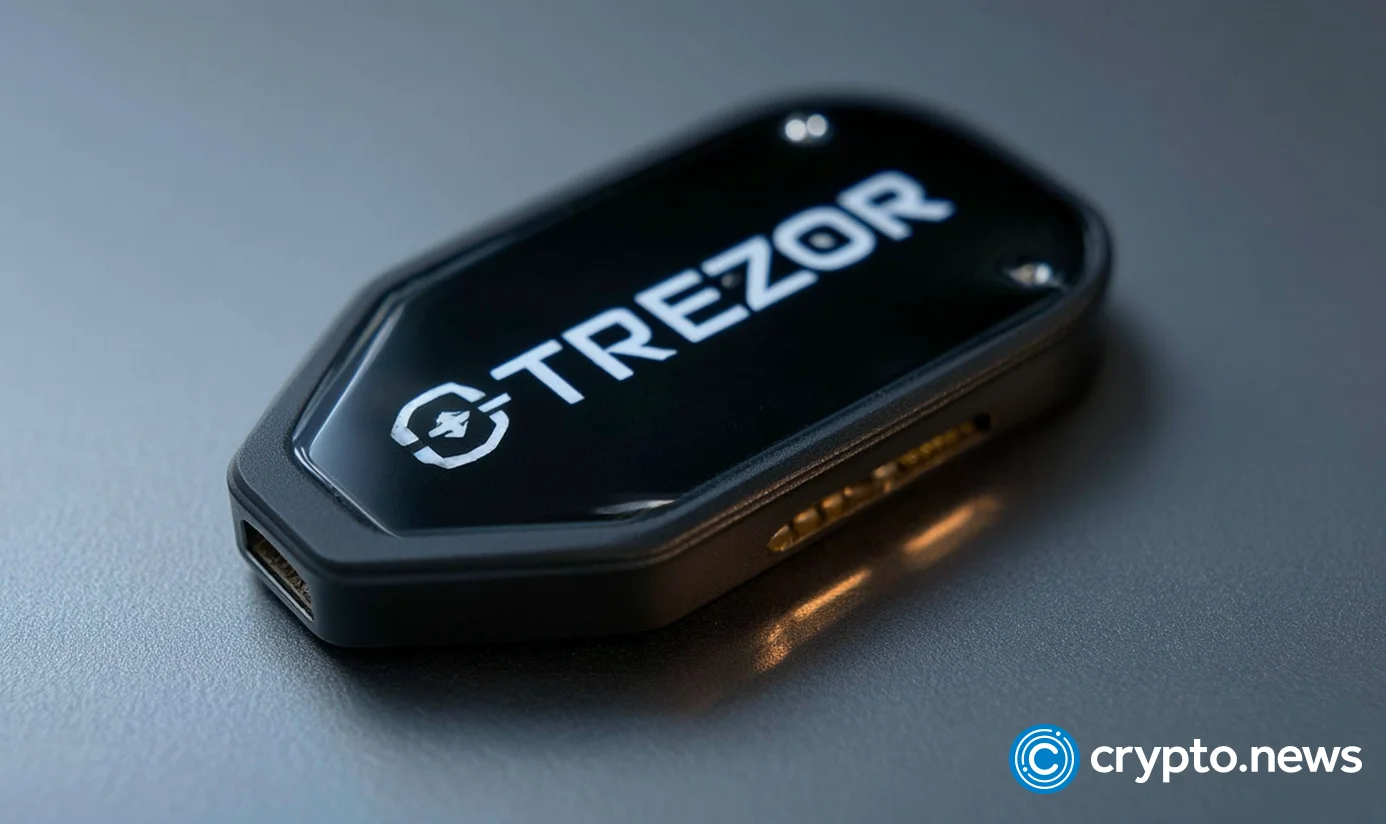
Trezor has cut its reseller network by roughly 80% and released a firmware update after finding hardware implants in three Safe 5 wallets purchased from former reseller CryptoBilis.
Summary
- Three Safe 5 wallets bought from CryptoBilis contained implants, according to Trezor’s investigation.
- Firmware version 2.13.1 blocks the identified implants, but previously captured recovery phrases remain exposed.
- Buyers from March 2026 onward remain eligible for replacements and should move funds to new wallets.
- No customers have reported losing funds, and no implants have been confirmed outside CryptoBilis.
Trezor’s Nov. 12 investigation update said customers should still move their cryptocurrency to a newly created wallet with a new seed, even after installing the protection released a day earlier.
The company said the removed resellers were trustworthy and posed no immediate threat. They did not meet the stricter handling requirements being introduced across its remaining partners, covering how devices are sourced, stored, and accessed.
Trezor firmware blocks implants but cannot protect exposed seeds
Released on Nov. 11, firmware version 2.13.1 prevents the implants identified during the investigation from capturing information on devices running the update, according to the wallet maker.
However, its instructions for CryptoBilis customers remain unchanged because recovery words collected before installation could already be exposed.
“If you bought from CryptoBilis, you should still move your funds to a new wallet with a new seed,” Trezor said.
In a reply on X, the company explained that the implant watches communication between the device’s microcontroller and display, then starts recording when it recognizes a particular sequence. Engineers changed the order of commands sent to the screen so that the trigger no longer works.
The earlier customer warning, covered by crypto.news after Trezor received the initial implant report, advised against importing the old recovery phrase into another hardware or software wallet.
Customers who have not configured a device bought from CryptoBilis were told not to set it up or enter an existing wallet backup.
Three affected wallets came from purchases in August and September
According to the investigation, all three affected Safe 5 devices were bought between Aug. 20 and Sept. 23, 2026, through CryptoBilis’s Tokopedia and Shopee stores or directly from the reseller.
Engineers examined the first reported device in Trezor’s laboratory. The other two implants were identified from photographs supplied by their owners.
Since its October appeal for customers to get in touch, the company has heard from 48 CryptoBilis buyers. Checks are being carried out through laboratory examinations or photographs of device internals.
Trezor said every other device examined showed no evidence of tampering. Inspections of wallets from other resellers in the region found none either, and the investigation has not confirmed an implant in another Trezor model.
The company removed CryptoBilis as an authorized reseller on Oct. 9 after reports of tampered Ledger wallets sold through the same business. Its first warning about a suspected Trezor implant followed on Oct. 30.
Hidden circuit boards captured recovery words from the screen
Trezor’s embedded engineering team extracted and analyzed firmware from the implant, which consists of an extra circuit board placed between the Safe 5’s main board and screen.
The company described a listening device that copies information displayed on the screen without changing the wallet’s own firmware or Secure Element.
It recognizes recovery words shown during the creation of a wallet backup, and words entered when restoring an existing wallet. Passphrases appearing on the screen can be captured in the same way.
According to the technical account, captured information is encrypted and transmitted over a mobile network to an attacker-controlled server. When a connection is unavailable, the implant stores the data and retries later.
Responding to questions about spotting tampering, Trezor said there were no obvious external differences. Opening a wallet can damage it, and a well-made implant can remain difficult to identify even with reference photographs.
Replacement eligibility starts with March purchases
Any customer who bought a Trezor from CryptoBilis from March 2026 onward qualifies for a replacement, a period extending beyond the purchase dates of the three identified devices.
Shipping restrictions may require a different model with the price difference refunded, delivery to an address in another country, or a refund. Customers should retain their devices and arrange assistance through Trezor Support.
The company warned that scammers may impersonate support staff offering replacements or refunds. Its staff will never ask customers to share their recovery phrases.